Understand your suppliers’ cyber risk. Strengthen your resilience.
Gain continuous visibility into the external cybersecurity posture of your suppliers and business partners. With RiskRecon by Mastercard, Infocredit Group helps you identify exposures, prioritise action and strengthen third-party oversight.
- Outside-in
- No agents or vendor cooperation needed
- Continuous
- Ratings refresh as footprints change
- From 10 vendors
- Packages sized to your portfolio
- Local support
- Onboarding & training by Infocredit Group
Your security depends on more than your own systems.
Suppliers and service providers connect to your data, systems and operations — and can introduce cyber exposure you don't directly control. Periodic questionnaires provide one part of the picture; ongoing external monitoring adds visibility between assessments.
- Assess suppliers before onboarding.
- Monitor external security posture over time.
- Prioritise findings based on risk.
- Support supplier reviews and remediation discussions.
- Provide evidence for management decisions.
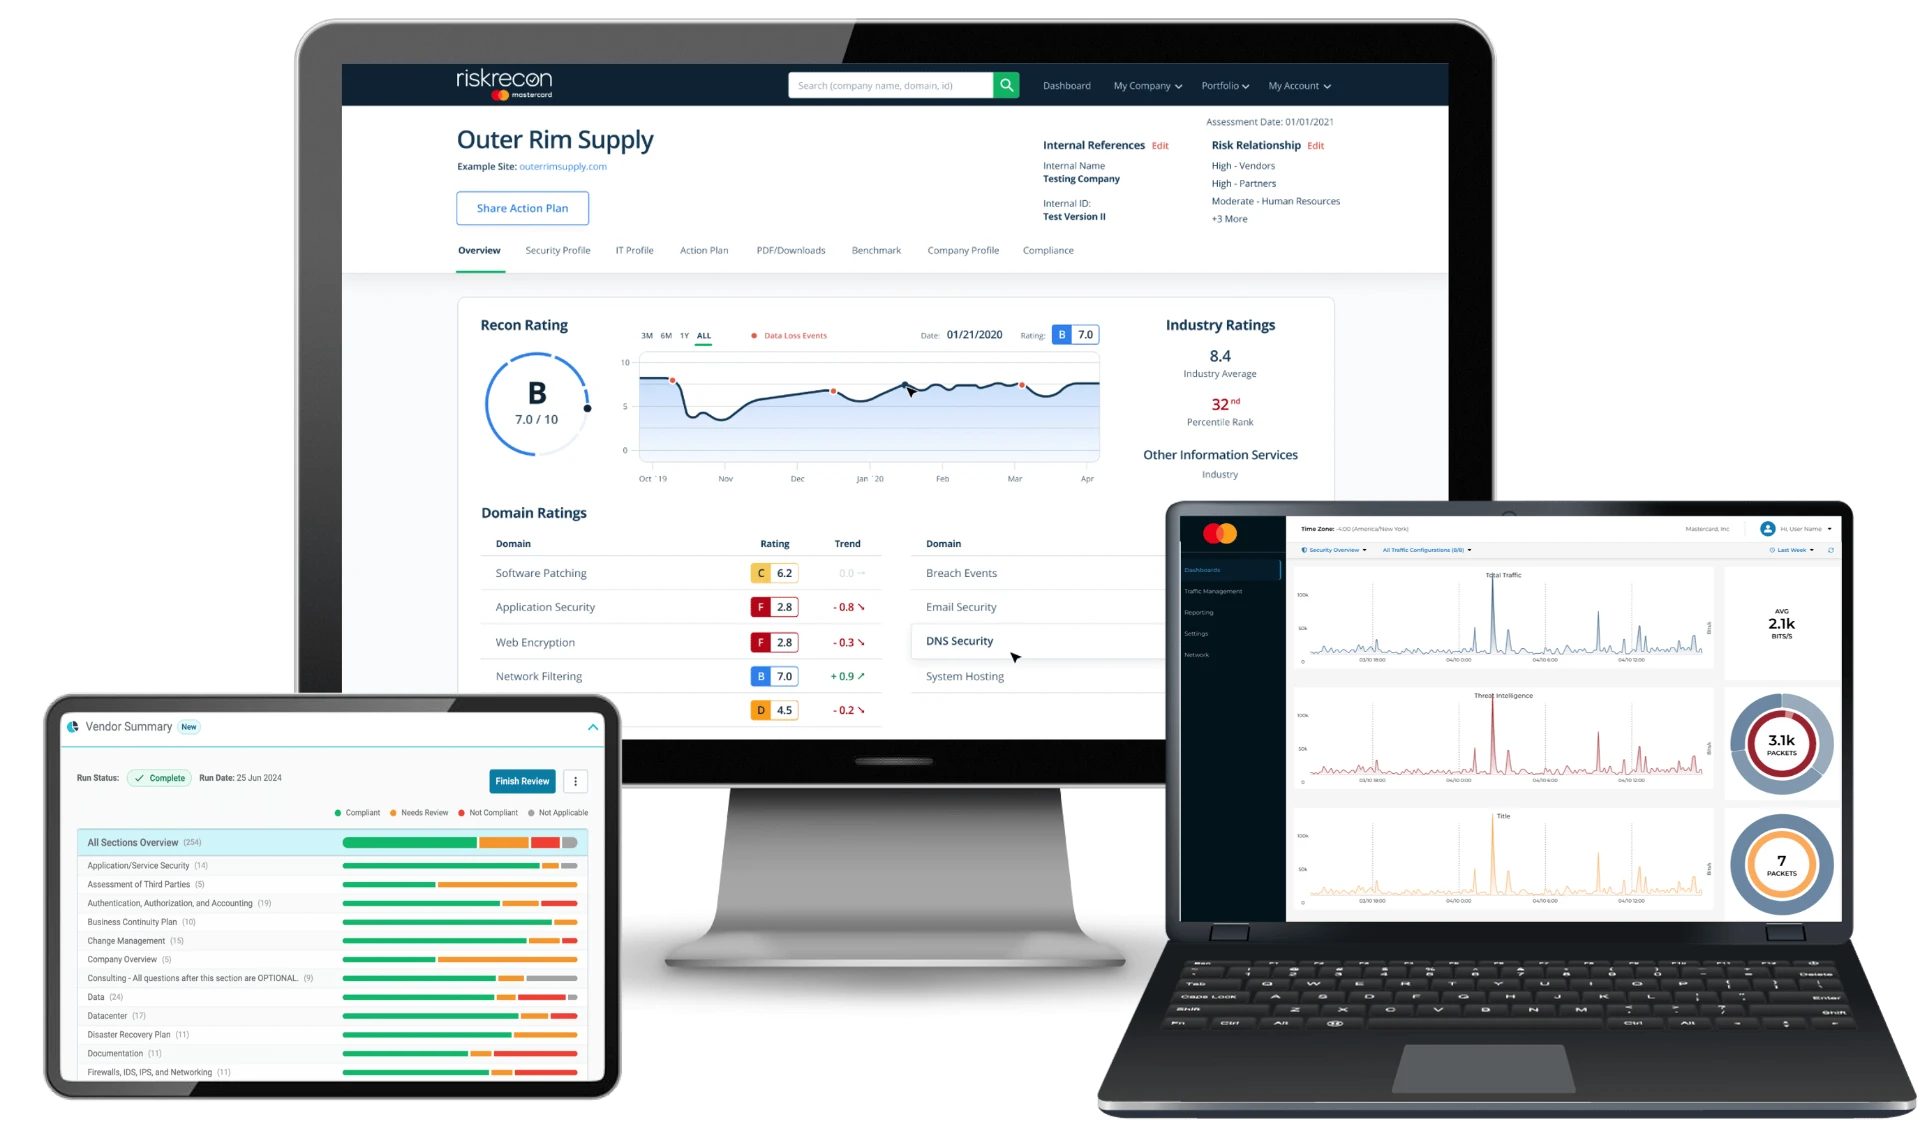 Illustrative view
Infocredit packages
Match the scope to your supplier portfolio.
Proposed annual subscription pricing, already discounted by 50% under the agreed Mastercard arrangement. Final commercial terms are confirmed in your quotation.
Essential
10 monitored vendors
€2,500per year
Support fee: €500
Growth
25 monitored vendors
€6,250per year
Support fee: €500
Advanced
50 monitored vendors
€10,500per year
Support fee: €1,000
Enterprise
100 monitored vendors
€17,500per year
Support fee: €1,000
Support is shown separately. Its scope and charging period, VAT treatment, contract duration and licence terms will be specified in the quotation. No funding approval or grant amount is included in these prices.
Questionnaires alone vs. adding continuous monitoring
What RiskRecon provides
External cybersecurity assessments
Objective assessments of a company's internet-facing systems, produced without requiring the vendor's cooperation.
Continuous vendor monitoring
Ratings and findings update as a vendor's externally observable footprint changes.
Portfolio visibility
View and compare your vendors on one consistent rating framework.
Risk-based prioritisation
Findings are weighted by issue severity and the value of the affected asset, so effort goes where exposure matters most.
Vendor action plans and remediation tracking
Share findings with vendors and follow remediation progress over time.
Management reporting
Summaries and vendor-level detail to support supplier reviews and management reporting.
External monitoring complements questionnaires, contractual safeguards, internal assessments and other due-diligence activities. Read more about RiskRecon.
NIS2 and ISO/IEC 27001
Support supply-chain cybersecurity oversight.
NIS2 includes supply-chain security within its cybersecurity risk-management measures. RiskRecon can support external supplier assessments, prioritisation and ongoing reviews.
- Supplier-risk assessment
- External security findings
- Ongoing supplier oversight
- Monitoring of posture changes
- Risk treatment
- Prioritised findings and remediation follow-up
- Management review
- Portfolio reporting
RiskRecon supports selected NIS2 risk-management activities. Full compliance also requires appropriate governance, policies, technical controls, incident processes and other applicable measures.
Planning a cybersecurity project under the Cyprus NIS2 funding call?
The published call targets SMEs designated by the Digital Security Authority as NIS2 Important Entities, and aims for DSA verification against CYFUN Basic (2025 edition). RiskRecon may form a supplier-risk monitoring component of a wider project, where justified by your organisation's assessed needs.
Inclusion of RiskRecon is subject to the call’s full conditions, eligible expenditure rules and project approval. Purchasing RiskRecon alone does not satisfy CYFUN Basic requirements.
- Funding per project
- €20,000–€100,000
- Published deadline
- 10 November 2026 at 13:00, or earlier if the budget is exhausted
- Applications
- Through the IRIS portal
Please check the official announcement for the call's latest status.
From product selection to practical supplier monitoring.
- 01
Discuss your supplier portfolio and critical dependencies.
- 02
Define the monitoring scope and suitable subscription.
- 03
Coordinate product onboarding and initial findings review.
- 04
Agree how monitoring will support ongoing supplier oversight.
Services are confirmed in the agreed proposal.
Frequently asked questions
What does RiskRecon assess?
RiskRecon assesses an organisation's internet-facing systems — such as websites, domains, email and network services — across multiple security domains. It is an external, outside-in view and does not audit internal controls.
How does it complement supplier questionnaires?
Questionnaires capture what a supplier reports at a point in time. RiskRecon adds independent, ongoing external observations between assessments, helping you validate answers and spot changes.
Can it support NIS2 and ISO/IEC 27001 activities?
Yes, for selected supplier-risk activities such as assessment, ongoing oversight, risk treatment and management review. It does not by itself establish NIS2 compliance or provide ISO/IEC 27001 certification.
Is RiskRecon automatically eligible for the Cyprus funding call?
No. Inclusion depends on the call's full conditions, eligible expenditure rules, your organisation's assessed needs and project approval. Purchasing RiskRecon alone does not satisfy CYFUN Basic requirements.
Does it replace penetration testing or internal security assessments?
No. External monitoring complements penetration testing, internal assessments, contractual safeguards and other due-diligence activities.
Can we purchase independently of a funding application?
Yes. RiskRecon is available through Infocredit Group whether or not you are applying for funding.
Bring your third-party cyber risk into focus.
Tell us about your supplier portfolio and cybersecurity priorities. Our team will help you explore the appropriate RiskRecon scope.